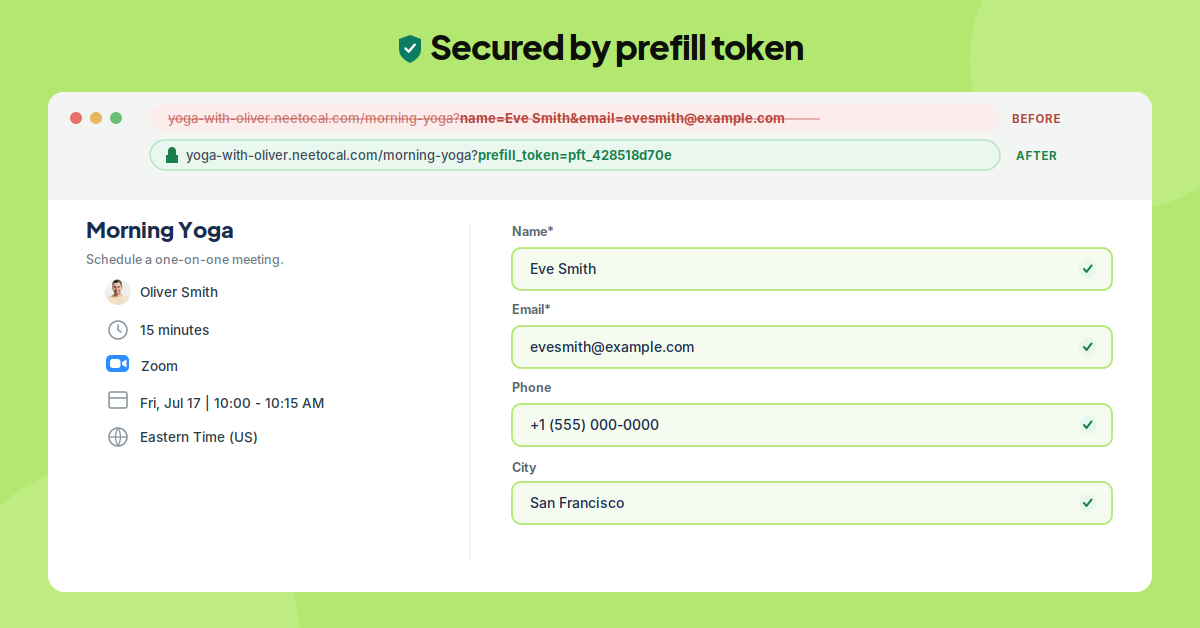
GDPR compliant way of prefilling booking questions with a secure token
You can now prefill booking questions without including your customer's personal details in the booking link. Instead of adding the customer's name and email as URL parameters, your website sends those details to NeetoCal behind the scenes and receives a secure prefill token in return.
Add this token to the booking link. When the customer opens the page, their booking questions are already prefilled, while their personal information never appears in the URL, browser history, or server logs. This makes prefilling GDPR compliant.
Each token remains valid for 30 days. Prefilling with URL parameters continues to work as before, but the token-based approach is the recommended option when handling personal information.
To learn more, read our help article.